

How Do I Change the Default Login Page in WordPress?
This tutorial has moved to the new WP Ghost Knowledge Base where each feature is presented in detail.
Enter a new name in WP Ghost > Change Paths > Login Security > Custom Login Path and click Save. Bots already know /wp-login.php, so moving the login page to a URL only you know takes it out of their reach. No files change, and you can switch back at any time.
How do I change the login path with WP Ghost?
Go to WP Ghost > Change Paths > Login Security. Enter your custom name in the Custom Login Path field. For example, instead of /wp-login.php you could use /my-secret-entry or any name that’s not easily guessable. Click Save.
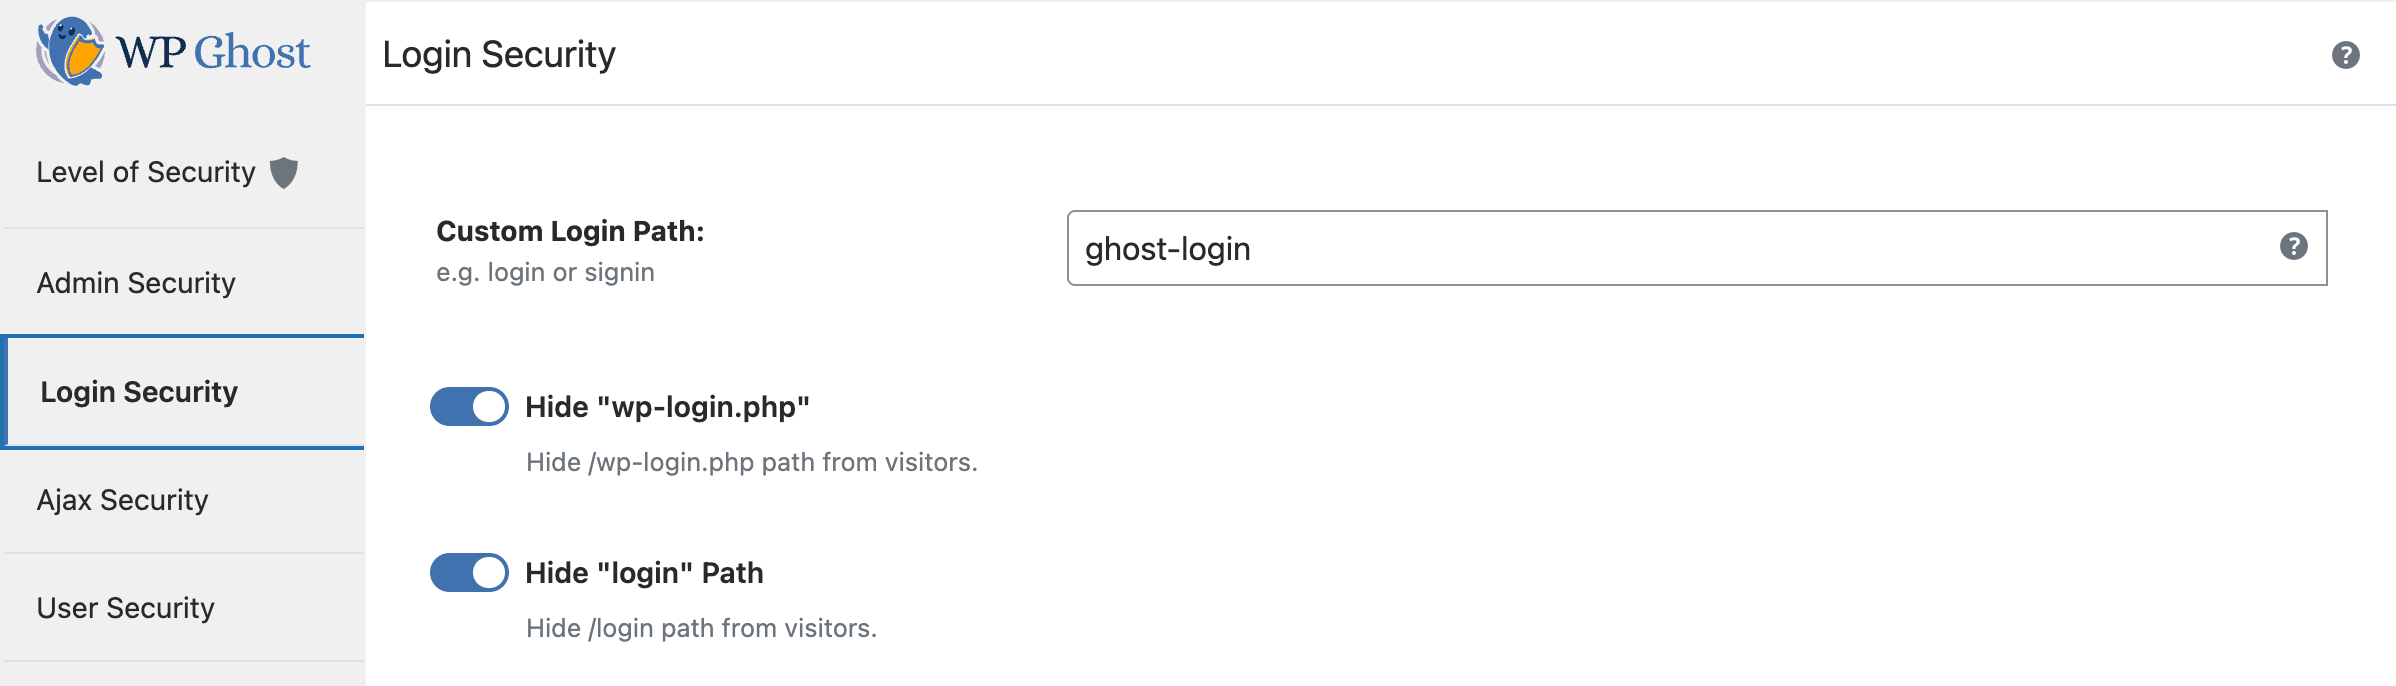
After saving, only your custom URL opens the login form. Bookmark it right away. To make the old /wp-login.php and /login paths return a 404 for visitors who aren’t logged in, switch on the two hide options described below.
WP Ghost does not physically change any files on your server. It uses rewrite rules to route requests from the new URL to the login handler. Deactivating WP Ghost restores the default login paths instantly.
What else should I do after changing the login path?
Changing the path is the first step. For complete login security, also enable these features in WP Ghost > Change Paths > Login Security:
Hide “wp-login.php” and Hide “login” Path: with these on, the old paths return a 404 for visitors who aren’t logged in. Without them, the old paths may still redirect to your new login URL, which gives it away.
Hide the New Login Path: hides the new login path from visitors and shows it only for direct access, so redirects don’t lead bots to it.
Then add brute force protection on top. Go to WP Ghost > Brute Force > Settings, enable Use Brute Force Protection, and select a reCAPTCHA type. This catches any attacker who somehow discovers your custom login URL. For the strongest login security, also enable two-factor authentication so that even a correct password isn’t enough to log in.
For the complete step-by-step guide with all options, see the change and hide login path tutorial.
Why is changing the login page so important?
The /wp-login.php path is the single most attacked page on any WordPress site. With WordPress powering over 43% of all websites, bots don’t need to discover your login page. They already know where it is. Automated brute force bots hit the default login URL thousands of times per hour, trying common username and password combinations. When that URL doesn’t exist, bots can’t find the login form and move on to the next target.
Changing the login path takes the busiest attack target off your site. Add brute force protection and 2FA, and automated login attacks have very little left to work with.
Frequently asked questions
What if I forget my custom login URL?
Bookmark it right after saving. If you forget it, open your Safe URL if you saved it, or use the emergency disable method: rename the plugin folder over FTP or add define(‘HMWP_DISABLE’, true); to wp-config.php, and the default /wp-login.php works again.
Will registration and password reset still work?
Yes. The wp-login.php file handles registration, password recovery, and user activation in addition to login. When you change the login path, all of these functions continue working through the new URL. You can also customize the register path and lost password path individually.
Does this work with WooCommerce?
Yes. Changing the WordPress login path doesn’t affect WooCommerce’s “My Account” customer login form. WooCommerce customer logins work independently. WP Ghost is fully compatible with WooCommerce, and brute force protection also covers WooCommerce login and registration forms.
Is this a free feature?
Yes. Changing and hiding the login path, brute force protection with every reCAPTCHA type, and hiding the old login paths are all in WP Ghost Free.
Does WP Ghost modify WordPress core files?
No. WP Ghost uses server rewrite rules and WordPress filters to change the login path. No files are moved, renamed, or modified. The wp-login.php file stays in your WordPress root. Deactivating WP Ghost restores the default login URL instantly.