How to Stop WordPress User Enumeration
November 5, 2026
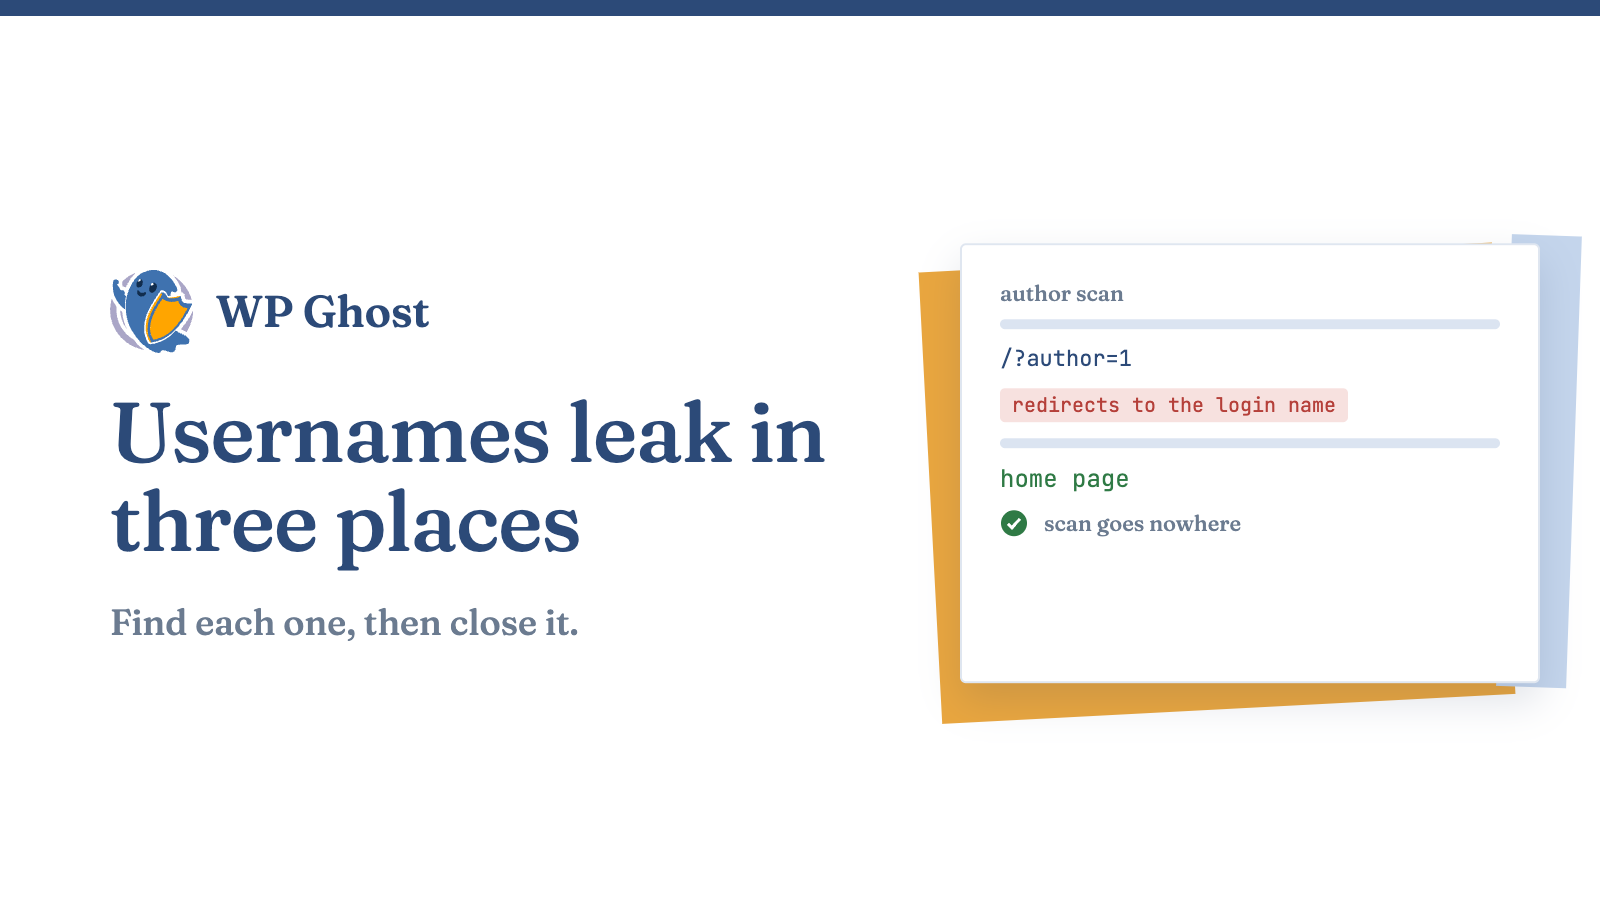
Type example.com/?author=1 into your address bar. If WordPress redirects you to a page with a username in the URL, you just enumerated your own admin.
That’s user enumeration. It hands attackers half of every login, so they only have to guess the password.
Where usernames leak
There are three common routes. The ?author=1 redirect works by counting through user IDs. The REST API lists authors at /wp-json/wp/v2/users. And the author archive pages, like /author/yourname/, print the login name right in the address.
Login error messages leak too. “The password you entered for the username admin is incorrect” confirms that “admin” exists.
Block the ?author= scan
Add this rule to .htaccess above the WordPress block. It sends the scan to the home page.
RewriteCond %{QUERY_STRING} ^author=([0-9]*)
RewriteRule .* /? [L,R=301]
Test it afterwards by loading /?author=1 again. You should land on your home page, not an author URL.
Close the REST API route
Anonymous visitors shouldn’t be able to list users. The steps are in the guide to restricting the WordPress REST API, which covers both a code snippet and a path change.
Change the author path
Public author archives put the login name in the URL. WP Ghost can change that path and swap the ID, and the author path guide has the steps.
The sitemap author listing leaks names too.
Make the display name different from the login
Go to Users, edit your profile and pick a display name that isn’t your login. Then change any admin account still named “admin” to something else. Create a new administrator, move the content over and delete the old one.
Stop the login form giving hints
Return one generic message for every failed login. A filter on login_errors that returns “Login failed.” does it.
Then turn on two-factor authentication.
Check your work
Run the three tests again. /?author=1, /wp-json/wp/v2/users and /author/yourname/ should all fail to show a login name. Do it in a private window so you see what a stranger sees.
FAQ
Is user enumeration dangerous?
On its own it breaks nothing. It makes password attacks cheaper, because the attacker already has the username.
Can I protect a multi-author blog?
Yes. Show author display names, and keep the login name out of URLs and the API.
How can I see enumeration attempts?
Look for requests to /?author= with rising numbers in your access logs.