

Is It Safe That I Can Access wp-admin While Logged In?
This tutorial has moved to the new WP Ghost Knowledge Base where each feature is presented in detail.
Yes, it’s safe. WP Ghost hides /wp-admin from visitors and bots who aren’t logged in, which is where attacks come from. Once you’re logged in, the default /wp-admin opens for you as well as your custom admin path.
How WP Ghost handles the admin path
WP Ghost’s path security is designed to block unauthenticated access, not authenticated access. When a bot or non-logged-in visitor tries to access /wp-admin, WP Ghost returns a 404 error or redirects them to a page you specify. The bot cannot confirm WordPress and moves on. When you are logged in as an administrator and visit /wp-admin, WP Ghost recognizes your authenticated session and lets you through. Your custom admin path also works, giving you two ways to reach the dashboard.

This dual-access approach exists for an important practical reason: if WP Ghost is deactivated (intentionally or due to an update conflict), the default /wp-admin path automatically becomes accessible again. If WP Ghost only allowed access through the custom path and something went wrong, you could be locked out of your own site. Keeping the default path accessible for authenticated administrators is a built-in safety net.
Restricting wp-admin for Non-Admin logged users
By default, every logged-in user (subscribers, contributors, authors, editors and administrators) can open /wp-admin. To keep the default admin path for administrators only, go to WP Ghost > Change Paths > Admin Security and switch on Hide “wp-admin” From Non-Admin Users. Logged-in users who aren’t administrators then get a 404 when they type /wp-admin.
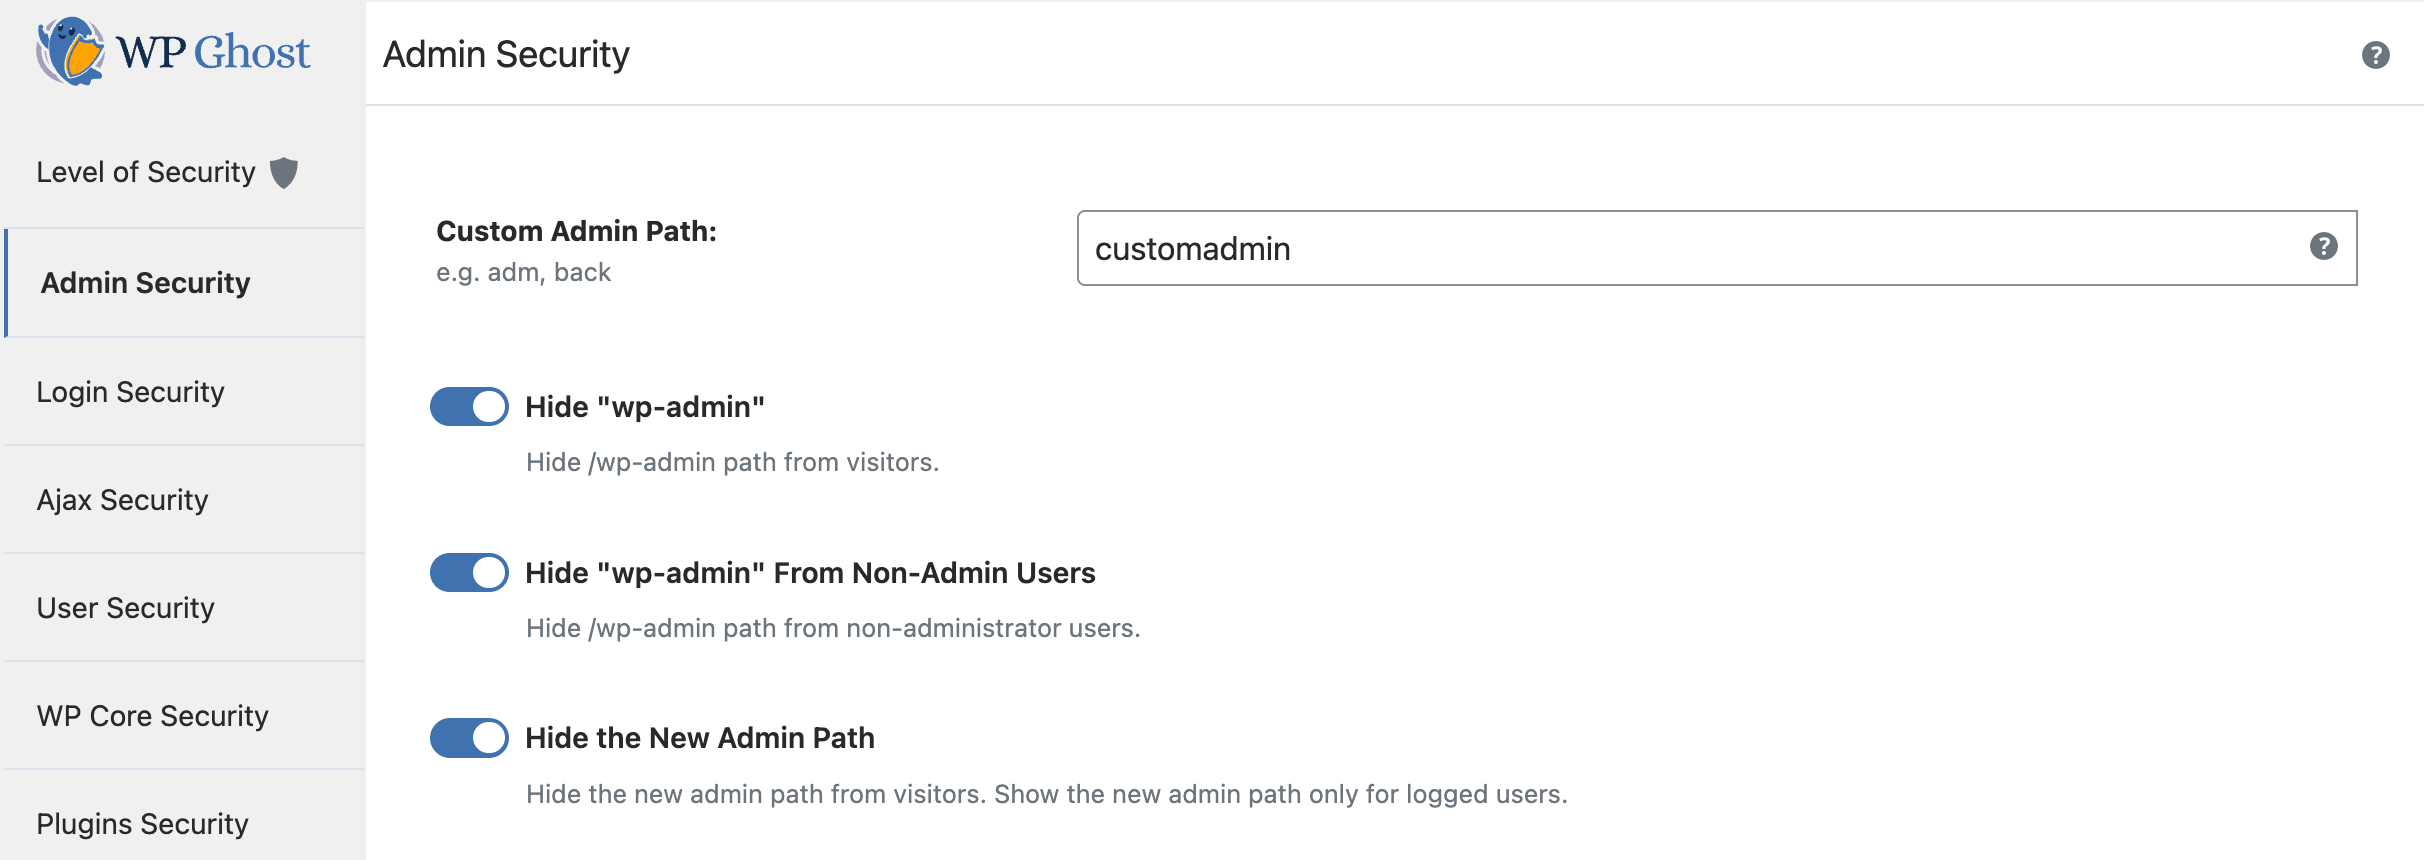
This is useful for membership sites, WooCommerce stores, and multi-author blogs where subscribers and customers should not see the admin backend. Those users can still access their profile pages and any frontend-facing dashboards provided by your theme or plugins. For the full admin path configuration, see the Change wp-admin Path tutorial.
Additional layers for admin security
The hidden admin path is one layer. For complete admin security, WP Ghost provides several additional protections that work together. Change the login path so bots cannot find the authentication form. Enable brute force protection with reCAPTCHA to limit login attempts on the custom login URL. Activate 2FA so even a compromised password doesn’t grant dashboard access. Enable security headers to protect against clickjacking on admin pages. With these layers on, only users who pass the login and 2FA checks reach the dashboard, whether they use the custom path or the default.
Frequently asked questions
Can bots discover that wp-admin is accessible for logged-in users?
No. Bots are not logged in. They send anonymous requests to /wp-admin and receive a 404 error or redirect. The authenticated access path is only available to users with a valid WordPress session cookie. Bots do not have that cookie.
Should I also hide wp-admin from the admin toolbar on the frontend?
The admin toolbar shows only to logged-in users, so visitors and bots never see it. If you don’t want logged-in users who aren’t administrators to open /wp-admin, switch on Hide “wp-admin” From Non-Admin Users; they get a 404 there.
What if I want only the custom path to work, not the default wp-admin?
You can enable Hide “wp-admin” in WP Ghost > Change Paths > Admin Security. This hides the default path for all non-logged-in users. For logged-in administrators, the default still works as a safety net. If you want to fully restrict the default path even for administrators, this is not recommended as it creates a lockout risk if WP Ghost is deactivated.
Does WP Ghost modify WordPress core files?
No. The wp-admin directory is not renamed or modified. WP Ghost uses server rewrite rules and session detection to control access. Deactivating the plugin restores normal access to /wp-admin for everyone.