How to Disable WP Ghost for Specific User Roles in WordPress
January 3, 2023
This tutorial has moved to the new WP Ghost Knowledge Base where each feature is presented in detail.
Quick summary: You can disable WP Ghost’s path security for specific user roles by adding a code snippet to your theme’s functions.php file. For IP-based access control, use the built-in whitelist feature in WP Ghost > Firewall > Whitelist instead.
Why disable WP Ghost for certain user roles
WP Ghost changes and secures WordPress paths for everyone visiting your site. That is exactly what you want for public visitors and bots. But in some situations, you may need certain logged-in users to see the original, unmodified WordPress paths instead.
This is useful when developers or editors need to debug frontend issues without path security interfering, when a third-party plugin expects standard WordPress paths for logged-in users, or when you want administrators to see the default site structure while non-logged visitors see the secured version.
WP Ghost provides two approaches: IP-based whitelisting through the dashboard (no code needed), and role-based disabling through a code snippet. Choose the one that fits your situation.
| Method | Best For | Code Required |
|---|---|---|
| IP Whitelist (dashboard) | Fixed team IPs, third-party services, debugging | No |
| Role-based disable (code) | Specific WordPress user roles regardless of IP | Yes |
Option 1: Use IP whitelisting (no code)
If your goal is to give specific people unrestricted access, the easiest approach is to whitelist their IP addresses. This requires no code and is managed entirely from the WP Ghost dashboard.
1. Go to WP Ghost > Firewall > Whitelist.
2. Under Whitelist Options, choose how WP Ghost treats those IPs: Allow access to hidden paths only, Show default WordPress paths and allow hidden paths, or Show default WordPress paths and disable all hiding.
3. Add the IP addresses you want to whitelist. You can use individual IPs or wildcard ranges like 192.168.0.*.
4. Click Save.
Whitelisted IPs bypass the firewall and the brute force limits, and the option you pick decides which paths they see. This is the recommended approach for teams with fixed IP addresses.
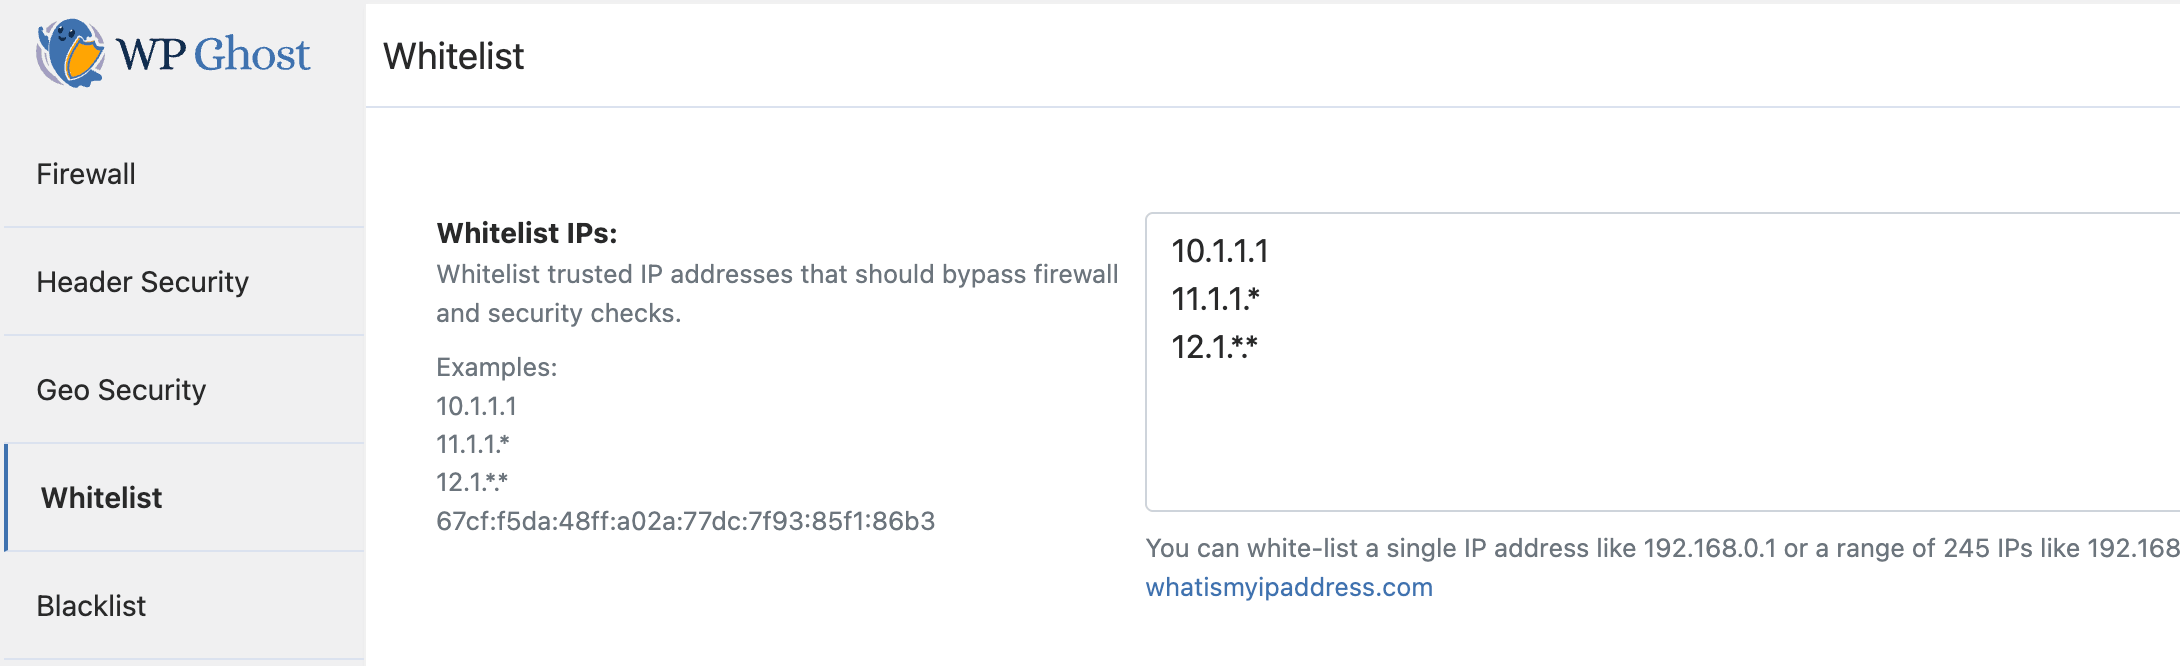
For a complete guide on whitelisting, including path whitelisting and all three whitelist levels, see the WP Ghost Whitelist tutorial.
Option 2: Disable path security by user role (code)
If you need to disable WP Ghost based on the user’s WordPress role rather than their IP address, add this code snippet to your active theme’s functions.php file or use a code snippets plugin.
The code snippet
function my_hmwp_skip_for_roles( $process ) {
    // The current user is known only after WordPress has loaded
    if ( ! did_action( 'init' ) || ! is_user_logged_in() ) {
        return $process;
    }
    $allowed_roles = array( 'administrator', 'editor', 'author' );
    if ( array_intersect( $allowed_roles, (array) wp_get_current_user()->roles ) ) {
        return false;
    }
    return $process;
}
add_filter( 'hmwp_process_buffer', 'my_hmwp_skip_for_roles' );
add_filter( 'hmwp_process_find_replace', 'my_hmwp_skip_for_roles' );
add_filter( 'hmwp_process_hide_disable', 'my_hmwp_skip_for_roles' );
This code turns off WP Ghost’s changes in the page output (custom paths and text mapping) and its hide and disable features for administrators, editors, and authors. The role check runs only after WordPress has loaded the current user. Visitors and any other roles still see the secured paths.
How to customize the roles
Edit the $allowed_roles array to match your needs. Add or remove roles as necessary. WordPress default roles you can use: administrator, editor, author, contributor, subscriber. If you use WooCommerce, you can also add shop_manager or customer.
For example, to disable path security only for administrators:
$allowed_roles = array(
    'administrator'
);
What the filters do
The code uses three WP Ghost filters that control different parts of WP Ghost’s processing:
hmwp_process_buffer controls whether the HTML output buffer is processed for path replacements. Setting it to false means the page HTML is sent as-is, without any URL rewriting.
hmwp_process_hide_disable controls the hide and disable features (disable right-click, view source and the like). Returning false turns them off for those roles.
hmwp_process_find_replace controls the path, text and URL mapping replacements in the page. Returning false skips them.
Together, these three filters turn off WP Ghost’s path changes in the page for the specified roles while keeping everything active for everyone else. You can drop a filter from the snippet if you want to keep that part of WP Ghost’s processing for those roles.
Where to add the code
You have two options. Add it to your child theme’s functions.php file (recommended – survives theme updates), or use a code snippets plugin that stores custom PHP independently of your theme.
Do not add this to your parent theme’s functions.php directly. A theme update will overwrite your changes.
Important considerations
This code only turns off the page changes and the hide and disable features for the specified roles. The firewall, brute force protection, 2FA and security headers stay active for everyone, including the roles listed in the code. To let a specific IP bypass the firewall and brute force checks too, add it to the IP whitelist instead.
The filters check is_user_logged_in(), so visitors who aren’t logged in never match a role, whatever page they open.
Keep in mind that users with the affected roles will see the real WordPress structure in the source code. If your security strategy relies on hiding paths from everyone, be selective about which roles you add.
Frequently asked questions
Should I use the code snippet or the IP whitelist?
Use the IP whitelist when you know the specific IP addresses of the people who need unrestricted access. It needs no code. Use the code snippet when access needs to be based on the user’s WordPress role regardless of which IP they connect from, like remote teams with dynamic IPs.
Does this affect the firewall and brute force protection?
No. The code snippet only turns off the changes in the page output and the hide and disable features. The firewall, brute force protection, 2FA and security headers stay active for the specified roles. A whitelisted IP is different: it bypasses the firewall and the brute force checks.
Will this code survive theme updates?
Only if you add it to a child theme or use a code snippets plugin. Adding it to the parent theme’s functions.php means a theme update will overwrite it. A child theme or snippets plugin keeps the code safe.
Can I use this with WooCommerce roles?
Yes. WooCommerce adds roles like customer and shop_manager. Add them to the $allowed_roles array in the code.
Does WP Ghost have a built-in setting for this?
WP Ghost has a built-in option to show or hide paths for all logged-in users: WP Ghost > Tweaks > Change Options > Change Paths for Logged Users. Check that option first. The code snippet gives finer control by targeting specific roles rather than all logged-in users.
Does WP Ghost modify WordPress core files?
No. WP Ghost uses WordPress hooks and server rewrite rules. No core files are modified. The code snippet in this tutorial also uses standard WordPress filters, which is the recommended way to customize plugin behavior.
Related tutorials
For more access control and customization options:
WP Ghost Whitelist (IPs and Paths) – Whitelist specific IPs and paths from the dashboard without code.
Disable WP Ghost on Specific Pages – Turn off path security on individual pages instead of by user role.
Customize Paths in WP Ghost – Full guide to all path security options including the “Change Paths for Logged Users” setting.
Grant User Role Access to WP Ghost Settings – Allow non-admin users to configure WP Ghost.
Brute Force Attack Protection – Login security that works alongside role-based path disabling.