Add Security Headers to WordPress with WP Ghost (HSTS, CSP, X-Frame-Options)
This tutorial has moved to the new WP Ghost Knowledge Base where each feature is presented in detail.
Add HTTP security headers to your WordPress site with one toggle in WP Ghost. Security headers tell browsers how to handle your site’s content and help block XSS attacks, clickjacking, MIME type sniffing and protocol downgrade attacks.
How to enable security headers in WP Ghost
Go to WP Ghost > Firewall > Header Security. Switch on Add Security Headers against XSS and Injection Attacks. Click Save.
WP Ghost sends the headers listed on the Header Security screen, and the Add Security Header button adds more. Every value can be edited there. After enabling, test your headers at SecurityHeaders.com to verify they are active.
Remove Unsafe Headers
Your server adds headers to every response that name your PHP version, the server software and its signature. Attackers read them to pick an exploit that fits your setup. Remove Unsafe Headers takes them out.
Go to WP Ghost > Firewall > Header Security. Switch on Remove Unsafe Headers. Click Save.
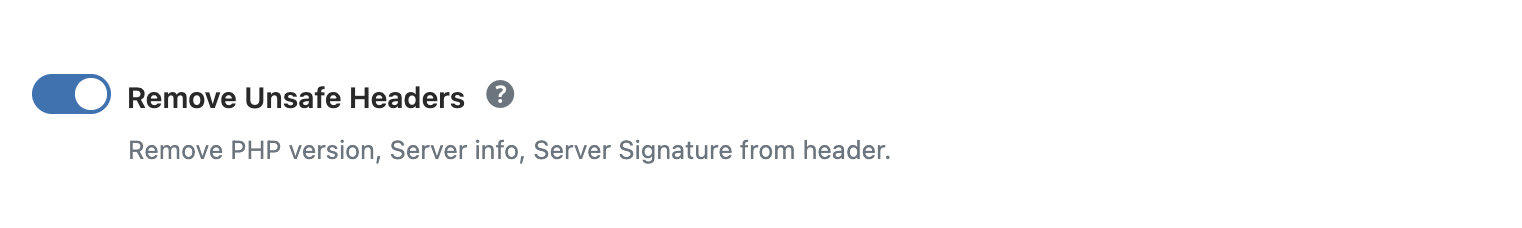
It removes the X-Powered-By header (your PHP version), the server info, the server signature and the WordPress-related headers. The security headers above aren’t affected, so you can use both.
Security headers reference
| Header | What it prevents | WP Ghost default |
|---|---|---|
| Strict-Transport-Security (HSTS) | Protocol downgrade attacks, cookie hijacking | max-age=63072000 |
| Content-Security-Policy (CSP) | XSS, unauthorized script execution | object-src ‘none’ (customize per site, see CSP tutorial) |
| X-Frame-Options | Clickjacking | SAMEORIGIN |
| Referrer-Policy | Leaking full page URLs to other sites | origin-when-cross-origin |
| X-Content-Type-Options | MIME type sniffing | nosniff |
| Cross-Origin-Embedder-Policy (COEP) | Data leaks through embedded content | unsafe-none |
| Cross-Origin-Opener-Policy (COOP) | Cross-origin information leaks, Spectre attacks | unsafe-none |
Content-Security-Policy (CSP)
CSP is the most complex of these headers. It controls which sources can load scripts, styles, images, and fonts on your pages. A restrictive CSP can block legitimate third-party scripts (Google Analytics, payment gateways, live chat). Test thoroughly after enabling. If a feature breaks, add the required domain to the appropriate CSP directive. See the Content Security Policy tutorial for examples and configuration.
Troubleshooting
A third-party service stopped working. Most likely CSP is blocking that domain’s scripts. Open browser DevTools Console (F12) to see which domain was blocked. Add it to the appropriate CSP directive in WP Ghost.
Page builder preview or iframes not loading. X-Frame-Options may be set to DENY. Change it to SAMEORIGIN to allow framing by your own domain.
Frequently asked questions
Which headers should I enable?
Start with Strict-Transport-Security and Content-Security-Policy, then add X-Content-Type-Options and X-Frame-Options and check the pages that embed content or load in frames. CSP is the one that usually needs extra domains for third-party services.
Do security headers affect performance?
No. Security headers are a few bytes in the HTTP response with zero impact on load time, rendering, or server performance.
Do security headers affect SEO?
Not directly. HSTS contributes to HTTPS enforcement which is a Google ranking signal. Google Lighthouse checks for security headers in its audit.
Does WP Ghost modify WordPress core files?
No. Headers are added through server configuration and PHP output. Disabling removes all headers instantly.