9G Firewall
This guide is for site owners and agencies who want to know what the 9G Firewall in WP Ghost does, see where it lives in the plugin, and switch to it.
TL;DR: 9G is the current generation of the WP Ghost firewall, built for how WordPress is attacked in 2026. It is the strongest Firewall Strength and the one new installs run by default. You set it in WP Ghost under Firewall & Headers by choosing 9G Firewall as your Firewall Strength, then saving and clearing your cache.
What the 9G Firewall is
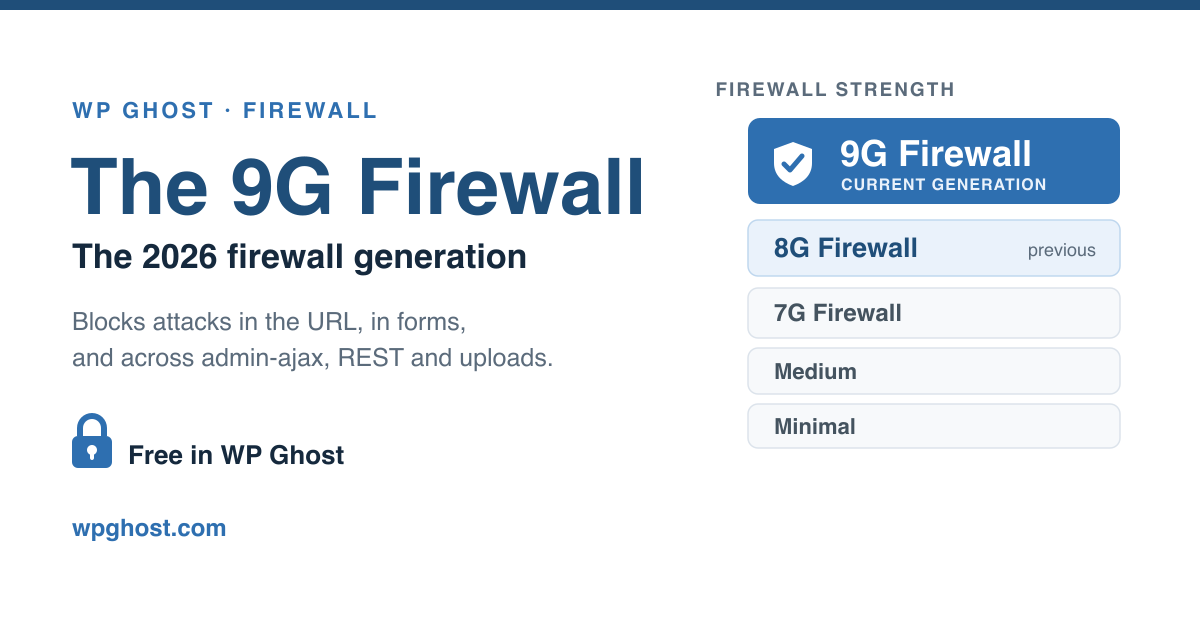
9G is the newest and strongest level in the Firewall Strength setting, after Minimal, Medium, 7G, and 8G. Think of 7G, 8G, and 9G as generations of the same firewall. Each one is a full rewrite for the threats of its time. 9G is the 2026 generation, and it is where every protection we add now lands.
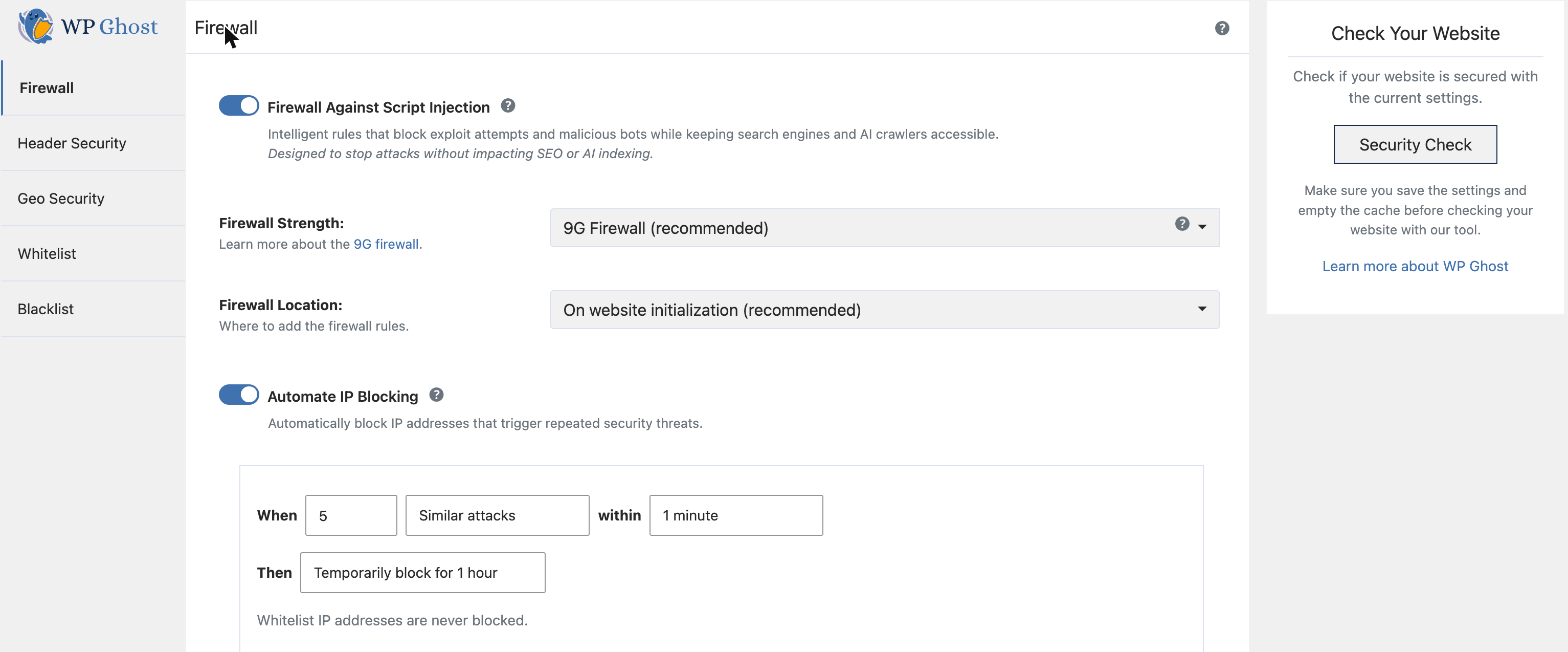
It sits on one screen in the plugin. Open WP Ghost, go to Firewall & Headers, and the Firewall Strength is the first thing on the page. New installs already show 9G Firewall (recommended).
That matters because the way WordPress gets attacked keeps moving. A firewall written for last year’s attacks blocks last year’s attacks. 9G is the level we keep current: when a new class of exploit shows up in the wild, the filter for it goes into 9G, and your site gets it on the next update with nothing to configure.
Where you set it
Firewall Strength is a single dropdown, so moving between generations is one choice. The levels run from Minimal up to 9G, and you can change your mind at any time from the same menu.
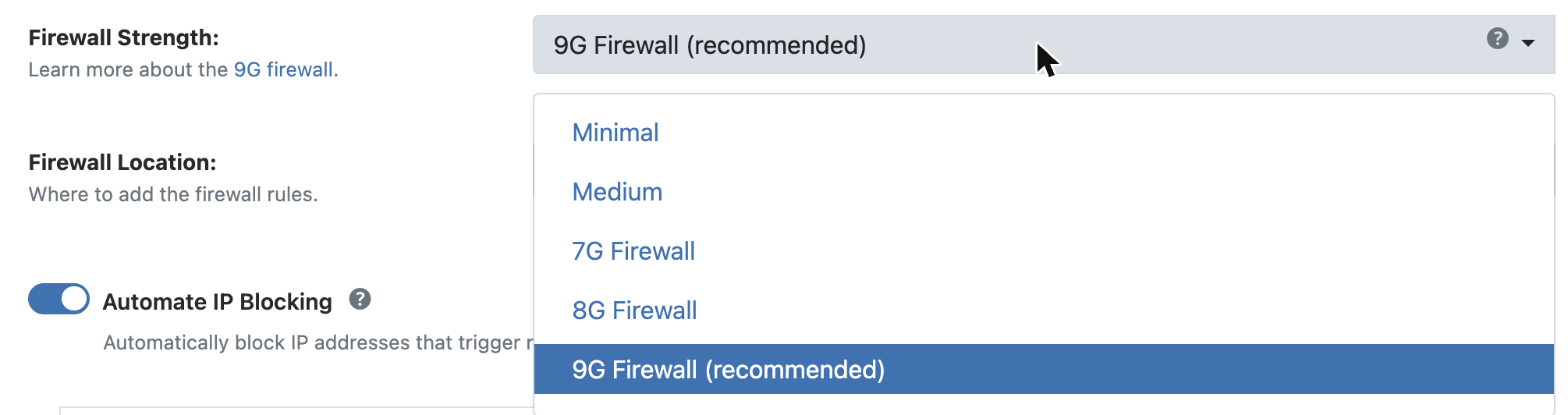
- Minimal and Medium. The light levels, for sites that need the fewest rules.
- 7G and 8G. The previous generations. They still block the attacks they were built for.
- 9G Firewall. The current generation, and the default on new installs.
Below the dropdown, Firewall Location lets you run the rules on website initialization, which is the recommended setting and the one that works on every host.
What the 9G Firewall protects against
9G covers the full range of how a WordPress site is probed and exploited, at the edge and inside the request:
- Injection and exploit patterns in the URL. SQL injection strings, cross-site scripting payloads, directory traversal, remote and local file inclusion, and malware-scanner probes are rejected by server-level rules before PHP even starts.
- Attacks carried in form and comment submissions. Comment forms, contact forms, and search fields are inspected for injection and code-execution payloads, while normal text goes through.
- admin-ajax and REST traffic. The endpoints that page builders, forms, and WooCommerce rely on are the doors most 2026 plugin exploits come through. 9G inspects them for a visitor; it does not for a logged-in editor.
- Malicious file uploads. A PHP file, or a PHP shell renamed to look like an image, is turned away before it can be saved and run.
- Account takeover at sign-up. A registration that tries to make itself an administrator or editor is refused. The account is still created as a normal customer.
- Object injection and server-side request forgery. Serialized PHP objects in a parameter, and requests aimed at internal or cloud metadata addresses, are blocked.
- Banned addresses, on every request. An IP on your ban list is blocked site-wide, on every request it makes.
I am describing these by what they stop. We do not publish the exact rules. They update with every WP Ghost release as new 2026 attack patterns appear, and the point of a firewall is that attackers never get the rulebook.
See it working: the Security Threats Log
In the premium version, every attack 9G turns away shows up in the Security Threats Log, under WP Ghost. Each row names the threat, the path and method, the country and IP, and marks it Prevented. It is the proof that the firewall is doing its job, and a quick read on what your site is actually being hit with.
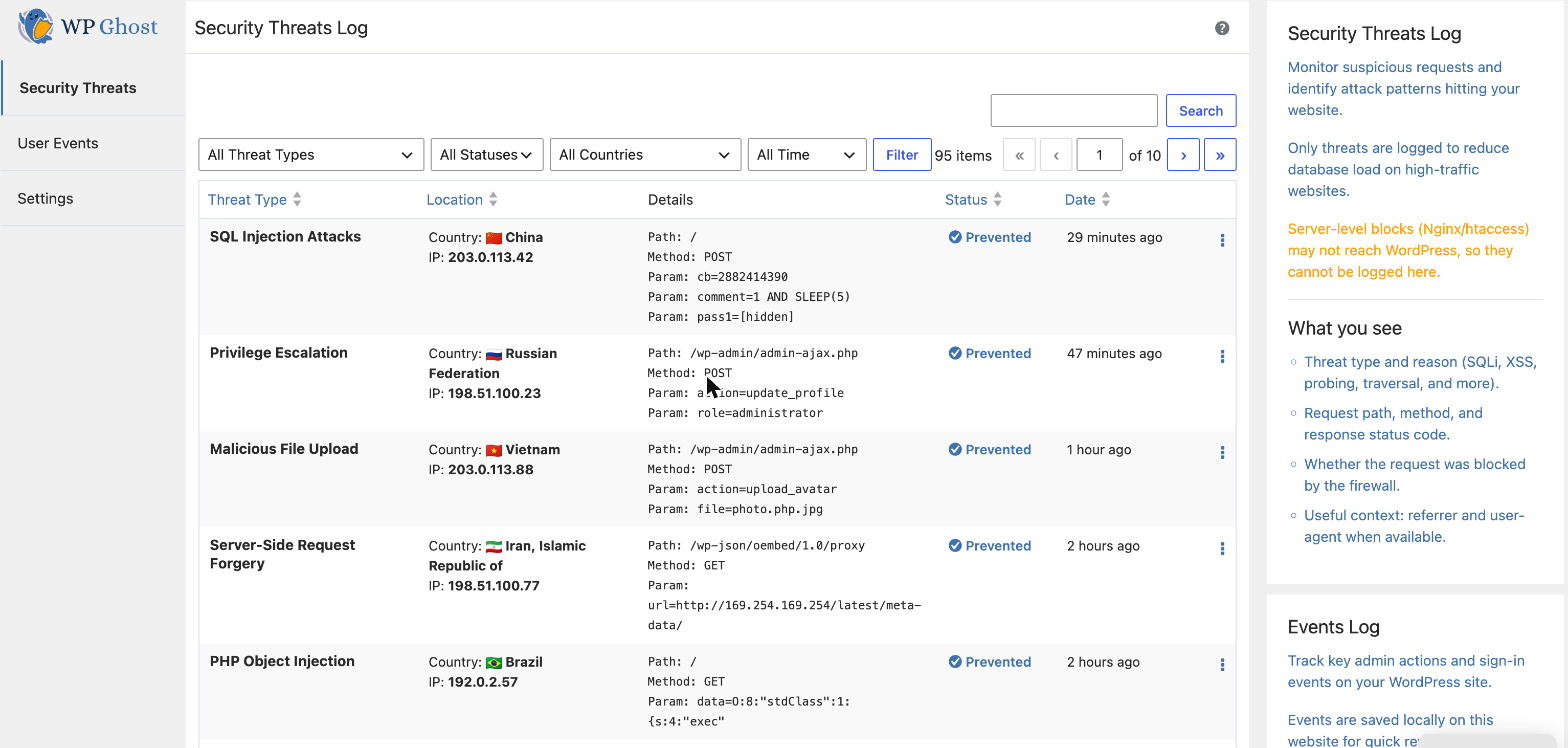
When an attack rides in on a login or checkout request, the log records it but redacts the sensitive fields. A password or card number reads as [hidden], so your incident log never becomes a place a secret leaks. The free version blocks the same attacks; the threats log, country data, and automatic IP banning are the premium additions on top.
Why this matters now
Patchstack’s State of WordPress Security in 2026 counted 11,334 new vulnerabilities disclosed in 2025, up 42% from the year before. 91% of them were in plugins. WordPress core accounted for the rest. And 45% of the heavily exploited ones were under attack within 24 hours of disclosure.
Most of those plugin bugs are not reached through the URL. They arrive through admin-ajax and the REST API, carried in the request body, which is exactly the traffic 9G was built to read. Patchstack’s own 2025 testing of common defenses found hosting and edge firewalls blocked as little as 12% of real exploit attempts. A firewall that only reads the URL line was never going to catch the rest. 9G does.
Turn on the 9G Firewall
- Open WP Ghost > Firewall & Headers.
- Set Firewall Strength to 9G Firewall.
- Click Save.
- Clear your cache so the change reaches every visitor.
New installs are already on 9G. If you are on an older level, switching takes effect at once, and you can drop back from the same menu if anything on your site needs it.
When the 9G Firewall is the right choice
- You run WooCommerce, a membership plugin, or a page builder. These lean on admin-ajax and REST, which is where 9G adds the most cover, and it keeps those calls working.
- You accept file uploads from visitors. Support forms and user profiles both take files; 9G rejects a disguised PHP upload before it lands.
- You want the protection we recommend and test first. 9G is the default on new installs and the level we validate each release against.
9G prevents attacks. It does not scan files for code that is already on disk, so pair it with a scanner like Wordfence or MalCare if you need cleanup after an infection. We are the lock on the door, not the cleanup crew.
FAQ
Will the 9G Firewall break WooCommerce or my page builder?
No. 9G reads admin-ajax and REST traffic, but it only rejects attack patterns, not normal calls. We test checkout, the block and classic checkout, and the common builders against 9G before every release. Logged-in editors and verified calls pass untouched.
Is the 9G Firewall in the free version?
Yes. 9G is in both the free plugin on wordpress.org and the premium version. Premium adds the threats log, country blocking, and automatic IP banning on top.
I already run 8G. Should I switch?
Yes, when you are ready. 8G is the previous generation and still blocks the URL-level attacks it was built for, but 9G is where the current protection and every new filter live. If you saved 8G, you keep it until you choose 9G from the Firewall Strength menu.
Does the 9G Firewall slow my site down?
No. The request checks run only on admin-ajax, REST, and upload requests, never on a cached page view, and only after the server rules have already turned away the obvious bad traffic. A normal page load has nothing extra to do.
Does 9G replace a malware scanner?
No. WP Ghost prevents attacks; it does not scan existing files for malware. For cleanup after an infection, pair it with a scanner. The two jobs are different.
Does the 9G Firewall work on nginx?
Yes. The request-inspection part of 9G runs inside WordPress, so it works on any server. The server-level rules it builds on are written automatically on Apache and LiteSpeed; on nginx you add the generated config once, as with any WP Ghost path change.
Will 9G keep getting new protection?
Yes. That is the point of the generation. New threat filters land in 9G with each WP Ghost release, so staying on 9G and keeping the plugin updated keeps you current without touching a setting.
If you have not set a Firewall Strength yet, open WP Ghost, go to Firewall & Headers, and pick 9G. WP Ghost has a free version on wordpress.org if you want to test it first.